AI Penetration Testing: How It Works and What It Finds
AI penetration testing lets you hunt for real security holes faster than a manual crew. Below we break down what it is, how it works, where it belongs, and what it can’t replace.
What Is AI Penetration Testing?
AI penetration testing is an authorized, offensive test that uses artificial‑intelligence to help or even run parts of the testing workflow. The NIST definition of penetration testing says it verifies how well a system resists active attempts to breach it, and AI adds automation to steps like reconnaissance, tool selection, and evidence collection.
In practice you’ll see two ends of a spectrum. On the low end, an AI assistant suggests test cases or parses logs for a human tester. On the high end, an agentic system can plan a multi‑step attack, execute it within a bounded scope, and adapt based on what it sees.
Our own team at Advatek runs AI‑augmented pentests for health‑tech clients. We let the AI do the heavy‑lifting of data‑intensive scanning, then our experts review the findings, add business context, and sign off on any exploit validation.
How AI Penetration Testing Finds and Validates Weaknesses
First, the AI crawls your assets, cloud configs, APIs, code repositories, and builds a map of the attack surface. It can parse thousands of configuration files in minutes, something a manual team would need days to do.
Next, it generates hypotheses. For example, it may spot a mis‑configured IAM role and then craft a credential‑stealing chain. The system runs the chain in a sandbox, watches the outcome, and records evidence. This mirrors the traditional discovery‑exploitation‑validation loop but at scale.
Validation still needs a human touch. The AI flags a potential path, but our engineers confirm whether the path works against real defenses and whether exploiting it would expose protected data. AI-only testing may miss the nuanced judgment a live red team brings.
By the end of a run, you have a prioritized list of exploitable findings, each with proof‑of‑concept steps and remediation guidance.
Key Takeaway: AI speeds up discovery and hypothesis generation, but human experts still verify exploitability and business impact.
Where AI Penetration Testing Fits in Healthcare and Other Regulated Businesses
Regulated sectors like healthcare, finance, and law firms must prove that technical controls protect sensitive data. AI-driven testing can help teams identify technical weaknesses and document findings for review.
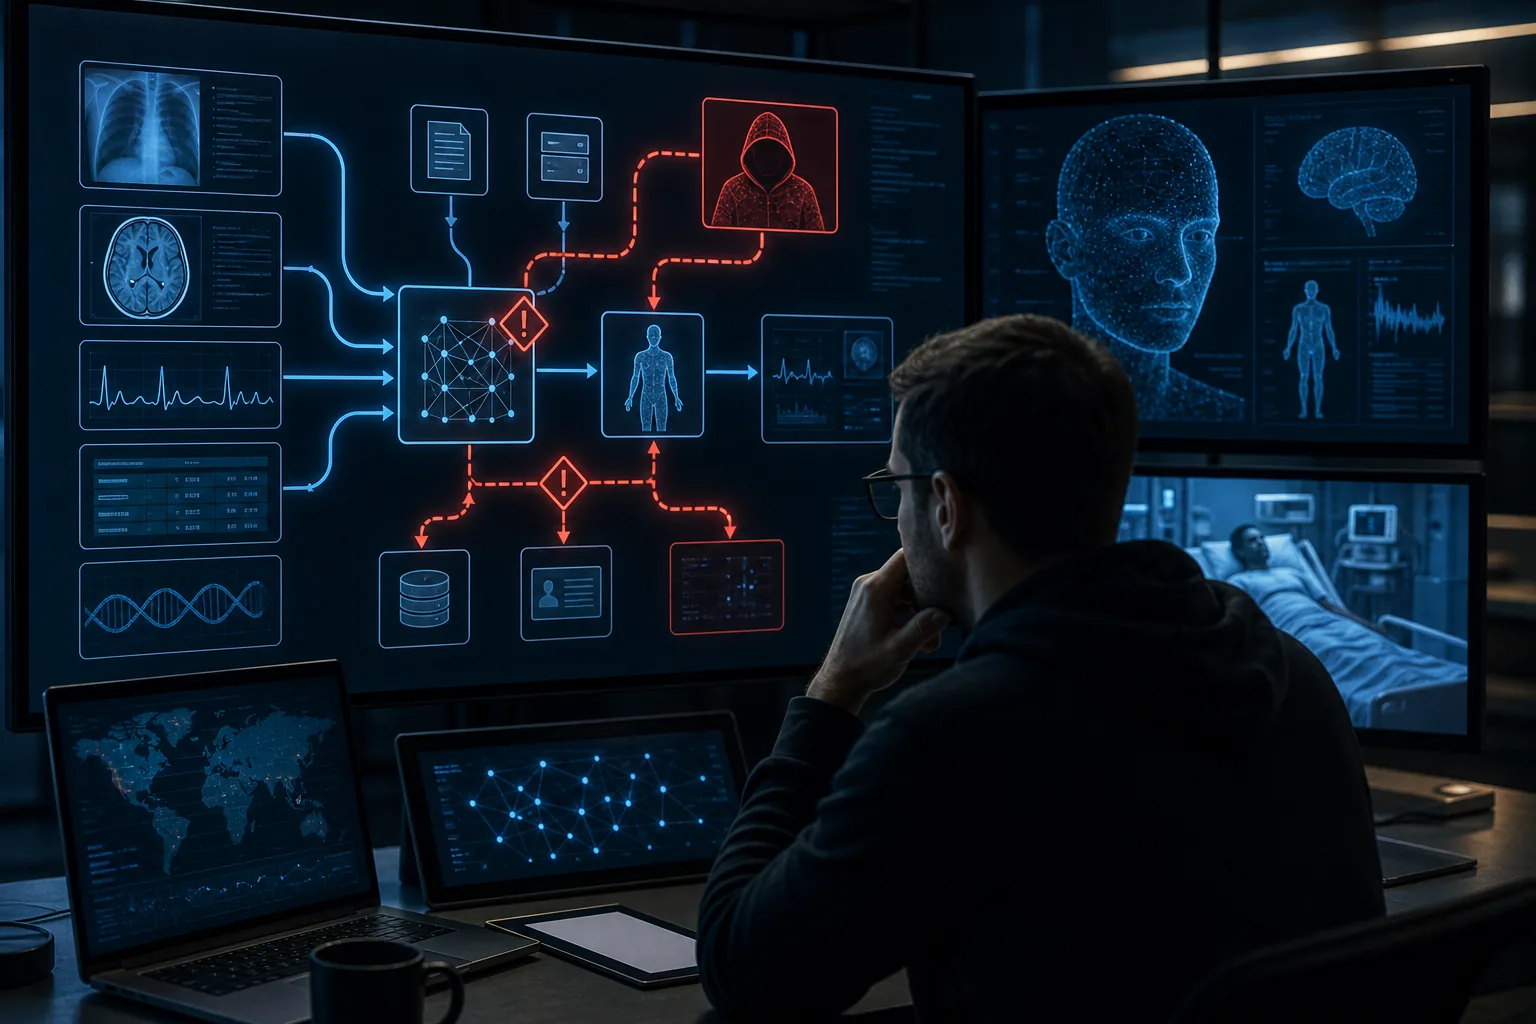
In a hospital network, AI can continuously scan new micro‑services, cloud storage buckets, and AI‑enabled clinical tools. When a new AI scribe feature goes live, the AI tester maps PHI flow, checks for prompt‑injection, and validates that no patient record leaks to another.
Law firms face similar pressures. The ABA calls for “reasonable efforts” to protect client data. An AI‑enhanced pentest can quickly surface insecure file‑sharing configurations or vulnerable third‑party integrations that a manual test might overlook.
Financial institutions can use AI-assisted testing to identify potential weaknesses, while qualified professionals review findings and determine how they fit into the organization’s security and compliance processes.
Our managed services team helps health‑tech firms align AI test outputs with HIPAA, SOC 2, and ISO 27001 risk registers, turning raw alerts into audit‑ready evidence.
Advatek’s managed‑IT expertise ensures the AI findings fit into your compliance workflow without breaking patient‑care schedules.
Risks and Limits: What AI Testing Cannot Replace
AI excels at scale but falls short on creative adaptation. Real attackers pivot on the fly, combine unrelated weaknesses, and exploit business‑logic flaws that a scripted AI model may never consider.
Human review can help validate high-impact findings. A qualified IT service provider can help interpret AI test results and determine what needs further investigation.
Another risk is false confidence. Dashboards that show “100 % coverage” often hide gaps in the AI’s knowledge base. Without an independent review, you might miss a novel vulnerability that the AI’s training data never saw.
AI tools can introduce risks if they run with privileged credentials. A qualified IT service provider can help manage testing access and reduce the risks of attempting implementation without professional guidance. For additional security guidance, consult a trusted IT professional.
Pro Tip: Pair AI‑generated findings with a manual red‑team exercise for any system that handles regulated data. The hybrid approach catches what either method alone would miss.
How an IT Service Provider Can Manage AI Penetration Testing
Choosing an MSP that knows both AI security and the compliance landscape saves you from hidden costs. The provider should set clear rules of engagement, isolate AI agents in a sandbox, and log every action for audit purposes.
We start with a scoping workshop. You tell us which assets hold ePHI, credit‑card data, or other regulated information. We then map data flows and define in‑scope versus out‑of‑scope boundaries.
Next, we deploy the AI engine on a dedicated Docker host or a managed cloud instance. Our team configures least‑privilege API keys, integrates with your CI/CD pipeline, and connects the output to a security‑information‑and‑event‑management (SIEM) system for real‑time correlation.
After each run, our analysts review the findings, enrich them with business context, and produce a compliance‑ready report. The report maps each finding to HIPAA, PCI‑DSS, or ISO 27001 control references, so you can hand it straight to auditors.
Because we handle the whole lifecycle, from planning to remediation tracking, you avoid the “DIY” trap of buying a tool, missing integration work, and then scrambling for evidence during an audit.
Advatek’s managed IT services include 24/7 monitoring, AI‑driven threat detection, and a dedicated compliance officer to keep your AI testing on the right side of the law.
FAQ
What is the difference between AI‑assisted and AI‑only penetration testing?
AI‑assisted testing uses AI to speed up tasks like scanning and hypothesis generation, but a human tester still validates exploitability. AI‑only testing runs the entire workflow without human oversight, which can miss nuanced attack paths and often fails compliance requirements.
Can AI penetration testing replace a traditional pentest for HIPAA compliance?
No. HIPAA requires documented technical evaluations and evidence of exploit validation. AI testing can provide supporting data, but a qualified human must sign off on the final report to meet audit standards.
How often should I run AI penetration tests on my cloud infrastructure?
Continuous testing works best for rapidly changing environments. At a minimum, schedule a full AI‑driven assessment after major deployments, configuration changes, or quarterly if your risk profile is high.
Do AI pentesting tools integrate with CI/CD pipelines?
Many do. Tools like Escape and Intruder can hook into GitHub or Azure DevOps to scan new code as it lands, generating alerts before a vulnerable change reaches production.
What should I look for in a vendor’s AI testing methodology?
Look for clear scoping rules, least‑privilege execution, documented validation steps, and evidence that the vendor maps findings to recognized frameworks such as NIST AI RMF or OWASP LLM Top 10.
Is AI penetration testing safe for live production systems?
Only when the engagement includes strict rate limits, approved credentials, and an emergency stop mechanism. Most providers, including Advatek, run tests in a controlled sandbox that mirrors production to avoid service disruption.
Conclusion
AI penetration testing gives you speed and scale, but you still need a skilled MSP to validate findings and keep you compliant. Contact Advatek to start a pilot that blends AI automation with expert oversight.
Download Franchise Information Report
Want to learn more about opening your own franchise? Fill out this form to get started: