Cybersecurity Risk Assessment Services: How to Run One
Running a risk assessment feels like a maze, but you don’t have to wander blind. Below is a step‑by‑step walk through the process, with Advatek leading the way.
Step 1: Define the Scope and Map Your Critical Assets
Every assessment starts by deciding what is in scope. List the systems, devices, cloud apps, and vendors that store or touch sensitive data, such as patient records or financial files, and name the person who owns each one. A narrow scope misses risks, while a scope that is too broad stalls the project before it starts.
At Advatek we connect this scoping work to our Cyber Security Services and 24/7 security monitoring, so the assessment ties back to the controls that protect your business every day. We work with healthcare providers, nursing homes, home health agencies, and other regulated organizations that need findings explained in plain language.
When you start with Advatek, expect a kickoff call that maps your critical assets, a vulnerability scan that runs while you’re treating patients, and a risk register that translates technical gaps into business language. The register lists owners, due dates, and the risk appetite you set, making the next board meeting a breeze.
Step 2: Identify Threats, Vulnerabilities, and Applicable Requirements
The first real work is to list what could go wrong. Think of every device that holds patient data, every cloud app you use, and every third‑party vendor you rely on. Threats range from ransomware to physical theft, while vulnerabilities include unpatched software and weak passwords. For healthcare firms, match each threat to the specific regulations you must meet, like HIPAA, HITECH, or state privacy laws.
We start by pulling logs from firewalls, endpoint agents, and email gateways. Those logs reveal unusual login spikes or data exfiltration attempts. Next, a qualified IT provider can help determine whether automated scanning is appropriate and interpret any findings. Finally, we map every finding to the relevant compliance clause so you can see exactly which rule is at risk. This step often uncovers low‑hanging gaps, a missing MFA on an admin portal or an unencrypted backup, that you can fix in a day.
Step 3: Evaluate Likelihood and Business Impact to Prioritize Risks
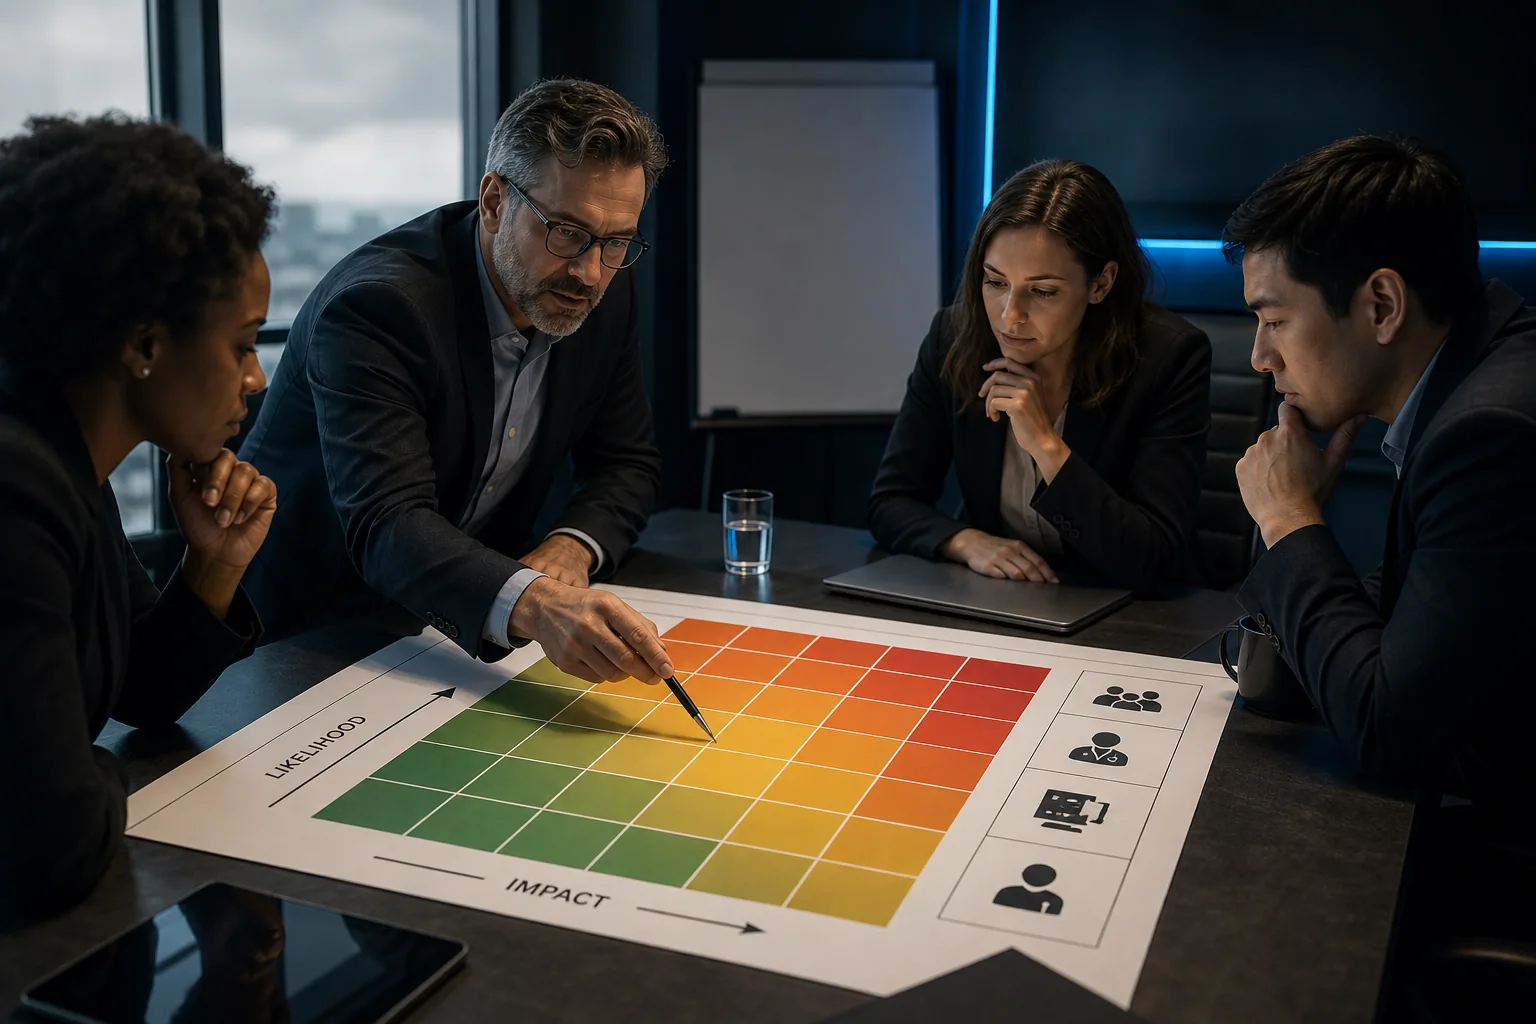
Not every finding deserves a full‑blown project. We score each risk by how likely it is to happen and how much damage it could cause to your operations. A risk matrix can help compare how likely an event is and how much it could affect operations. The impact side looks at downtime cost, regulatory fines, and reputation loss.
For example, a missing patch on a critical EHR server might have a high likelihood (known exploits circulate) and a high impact (patient records become inaccessible). That risk lands at the top of the list and gets an immediate remediation plan. In contrast, a low‑severity misconfiguration on a test server might sit lower because the chance of exploitation is slim and the business effect is limited.
Key Takeaway: Pairing likelihood with concrete business impact turns a long list of flaws into a focused, budget‑friendly roadmap.
When the scores are in, we rank the risks and hand you a prioritized register that shows who owns each item and when it should be resolved. This register becomes the single source of truth for both IT and compliance teams.
Step 4: Build a Risk Treatment Plan With Owners and Timelines
Now that you know what to fix, you need a plan that tells who does what and by when. Advatek works with your leadership to assign each risk to a functional owner, IT, clinical staff, or a third‑party vendor. The timeline reflects your risk appetite and any compliance deadlines you face.
We draft a treatment plan that includes three columns: the risk description, the remediation action, and the target date. For each action we also note the required resources, whether it’s a policy update, a technical fix, or a vendor contract review. This format creates a ranked treatment plan that’s easy for executives to read and for the IT team to execute.
During this stage we also set up tracking checkpoints. Every month the owner reports progress, and we adjust the plan if new threats emerge. A common pitfall is to skip the owner‑sign‑off step, which leaves remediation hanging. By locking in responsibility early, you avoid that trap.
Pro Tip: Pair each remediation item with a measurable success metric, like “patch applied on 100% of workstations”, so you can prove closure during audits.
Step 5: Review Findings With an IT Provider and Reassess Regularly
After the treatment plan is live, you need a fresh set of eyes to verify that fixes are effective. Advatek schedules a formal review where we walk through the risk register, demonstrate the implemented controls, and answer any auditor questions. This review often uncovers gaps that were missed in the first pass, especially after a system upgrade or a new vendor onboarding.
Continuous reassessment is key. Threat landscapes shift, new ransomware strains appear, and regulatory updates add fresh requirements. We recommend a quarterly mini‑assessment that re‑runs the vulnerability scans and updates the likelihood scores. That way the risk register stays current and you can justify security spending to the board with real data.
If you choose to work with another IT provider, make sure they adopt the same structured approach, otherwise you’ll end up with duplicate reports and wasted effort. The goal is a single, living document that guides security decisions for years to come.
Frequently Asked Questions About Cybersecurity Risk Assessment Services
What is a cybersecurity risk assessment?
A cybersecurity risk assessment is a systematic review that identifies threats, evaluates vulnerabilities, and ranks risks based on likelihood and business impact.
How often should I run a risk assessment?
You should conduct a full assessment at least annually and anytime you add new systems, change vendors, or experience a security incident.
Do I need a separate assessment for HIPAA compliance?
Yes. HIPAA requires a dedicated security risk analysis that covers ePHI. A HIPAA risk assessment checklist can help healthcare teams organize the steps, document safeguards, and identify gaps; a qualified IT provider can help apply it to your systems and compliance needs.
Can I do a risk assessment myself?
You can start with a free self‑assessment tool, but a professional service adds depth, validates findings, and produces an audit‑ready report.
What does Advatek do differently?
Advatek combines AI‑driven threat detection with industry‑specific compliance expertise, delivering a risk register that links technical gaps directly to regulatory requirements.
Conclusion
Start with Advatek’s AI‑enhanced risk assessment to get a clear, prioritized roadmap, then follow the five steps to keep your security posture aligned with business goals. Reach out for a free assessment and we can start the first draft of your risk register.
Download Franchise Information Report
Want to learn more about opening your own franchise? Fill out this form to get started: