HIPAA Email Rules: How to Stay Compliant
One missed email can cost a small practice millions. Below is a step‑by‑step walk‑through that gets every part of the HIPAA email rules under control.
Step 1: Identify When HIPAA Email Rules Apply
First, confirm you’re a covered entity or a business associate. That means you’re a health plan, a health‑care clearinghouse, a provider, or a vendor that handles PHI on behalf of one of those groups. If you’re not in one of those categories, the email rules don’t bind you.
Next, check every email for PHI. The rule only kicks in when the message creates, receives, stores, or transmits protected health information. A plain appointment reminder without any patient data falls outside the scope, but a lab result attached to an email does not.
State laws can add “affirmative opt‑in” requirements. Several states, including Connecticut, Texas, and Virginia, require written consent before you can email PHI. When a patient asks for a different way to communicate, you must honor it and document the request.
We recommend treating all outbound mail as if it contains PHI until you’ve documented an exception. That eliminates the risky “case‑by‑case” guessing game.
Advatek’s Managed IT & HIPAA Compliance Services include a policy audit that maps exactly which of your email flows fall under the rule, so you never miss a vulnerable channel. Our HIPAA compliance checklist walks you through that discovery phase.
Step 2: Protect PHI With Secure Email and Communication Safeguards
Encryption is the backbone of any HIPAA‑compliant email strategy. It must make the content unreadable to anyone without the proper key, whether the message is in transit or stored at rest.
Beyond encryption, you need strong access controls. Every user gets a unique ID, a strong password, and multi‑factor authentication. Role‑based permissions keep staff from seeing more PHI than their job requires.
Audit logging rounds out the picture. Each send, receive, and delete event gets a timestamp and a user tag. Those logs become the evidence you show during an OCR audit.
Don’t forget mobile messaging. Standard SMS is plain text and fails the encryption test. Use a secure, encrypted SMS gateway or a HIPAA‑ready messaging app that logs every exchange.
Finally, lock down the network path. Transport Layer Security (TLS) encrypts the server‑to‑server hop, and email encryption helps protect PHI.
Step 3: Choose and Configure the Right Email Encryption
Microsoft 365 offers several built‑in options. Pick the one that matches your workflow and your recipients’ capabilities.
| Option | How It Works | Pros | Cons |
|---|---|---|---|
| Microsoft Purview Message Encryption | Server‑side encryption that can be opened in a web browser. | Works with any recipient; no extra client needed. | Limited control over branding. |
| S/MIME | Certificates embed a public key in the message header. | Strong end‑to‑end security; integrates with Outlook. | Requires certificate management for each user. |
| Information Rights Management (IRM) | Applies usage rights that persist after decryption. | Can prevent forwarding or printing. | Only works within the Microsoft ecosystem. |
| TLS | Encrypts the channel between mail servers. | Enabled by default; no user action. | Does not protect the message body. |
| PGP (Inline) | Encrypts the body with a public key; recipient uses a private key. | Industry‑standard cryptography. | Not supported for PGP/MIME; can break compatibility. |
Our experience shows that layering more than one technology on the same email often causes delivery failures. Don’t apply multiple email encryption technologies to the same email message.
Advatek handles the whole setup: we generate certificates, configure Purview policies, and test compatibility with the most common client apps. The result is a smooth experience for clinicians and a clean audit trail for compliance officers.
Step 4: Set Email Retention, Access, and Workforce Policies
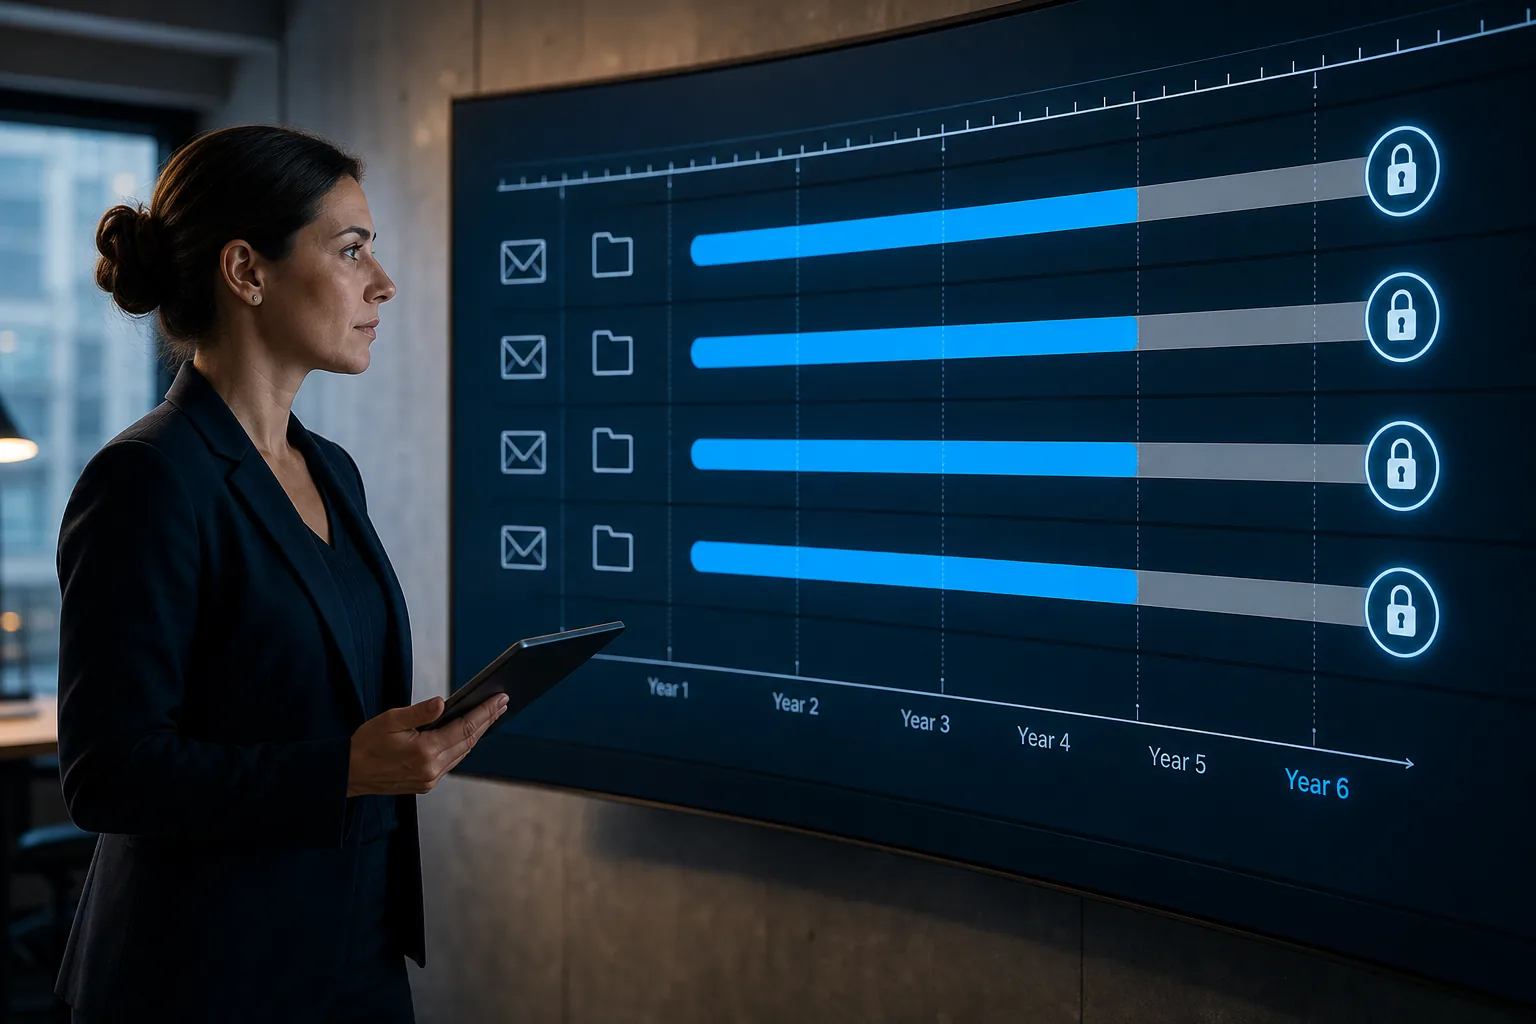
HIPAA requires you to keep any email that contains PHI for at least six years. That includes inbound, outbound, and archived copies. An email retention schedule spells out how long each type of message stays alive and who can delete it.
Access controls tie directly into that schedule. Only authorized staff can open or export retained messages. Audit logs record every view, export, and deletion attempt.
Training is the third pillar. Your workforce must know the minimum‑necessary rule, how to request alternative communication methods, and how to flag a message that should not be sent via email.
Advatek provides a ready‑made policy template that aligns with the HIPAA Security Rule and the six‑year retention mandate. Our secure‑email hosting guide shows how the policy plugs into the technical controls you already have.
Step 5: Test, Monitor, and Manage HIPAA Email Compliance
Testing starts with a risk assessment. Simulate a PHI email flow, then try to intercept it. If the interceptor can read the content, you’ve missed a protection layer.
Continuous monitoring catches drift. Set up alerts for unencrypted outbound messages, failed MFA attempts, or changes to encryption policies. Those alerts feed into a central dashboard that shows compliance health at a glance.
When a violation occurs, the breach notification rule demands you inform the patient within 60 days if you can’t get consent for electronic notice. Keep a template ready and automate the trigger from your monitoring system.
Advatek’s 24/7 security operations center watches those alerts in real time, escalates any breach, and provides the documentation you need for an OCR audit. That way compliance becomes a state you stay in, not a scramble before an inspection.
FAQ
Do I need to encrypt every email I send?
No. Only emails that contain PHI fall under the rule. However, many practices choose to encrypt all outbound mail to avoid accidental leaks.
What counts as PHI in an email?
PHI includes any individually identifiable health information, names, dates of birth, test results, or even a unique patient ID, when it appears in the message body or an attachment.
Can I use Gmail for HIPAA‑compliant email?
Gmail can be HIPAA‑compliant only if you sign a Business Associate Agreement and enable the required security settings. Advatek can help you set up the BAA and configure the necessary controls.
How long must I keep PHI‑containing emails?
HIPAA mandates a minimum retention period of six years for any email that includes PHI, regardless of whether the email is stored on‑premise or in the cloud.
What if a state law is stricter than HIPAA?
State laws that offer greater protection or more rights for patients preempt HIPAA, so you must follow the stricter rule.
Do I need a separate policy for mobile texting?
Yes. Text messages are treated as ePHI under the Security Rule, so you must use an encrypted, BAA‑covered texting solution and train staff on consent and logging.
By following these steps, you turn a complex set of regulations into a repeatable process.
Conclusion
Start with Advatek’s managed compliance audit to map every email flow, then implement the encryption and retention controls we outlined. Reach out to our team today for a free risk assessment and get your practice HIPAA‑ready.
Download Franchise Information Report
Want to learn more about opening your own franchise? Fill out this form to get started: