Best HIPAA Compliant Fax Service Options
A fax can move patient records in seconds, but the wrong plan can leave your practice exposed. The leading options can be compared for BAAs, encryption, audit trails, integrations, and day-to-day fit. Here are the best HIPAA compliant fax service options, with a clear use case and caveat for each. Table of Contents Advatek: Managed […]
What Is a Business Associate Agreement? HIPAA Guide
Someone asks your healthcare business to sign a BAA, and suddenly a simple vendor deal feels much more serious. A business associate agreement is a contract that sets rules for handling protected health information, or PHI. We’ll show you who needs one, what it must say, and how to manage it after signing. Table of […]
Best HIPAA Compliance Software: 8 Top Picks
HIPAA work gets messy fast. You need to protect patient data while keeping up with risk reviews, staff training, vendor agreements, and security alerts. Advatek is a managed option for teams that want managed help instead of another dashboard to run. Table of Contents Advatek Vanta, broad compliance automation for growing companies Drata, continuous monitoring […]
What Happens If You Violate HIPAA?
A HIPAA violation can lead to corrective action, civil fines, breach notices, and in serious cases, criminal charges. The financial range can run from a modest penalty to an $865,500 settlement. We’ll walk through what to do after a suspected violation, how to assess reporting duties, and where managed IT services can reduce the damage. […]
How to Build a SaaS Management Plan
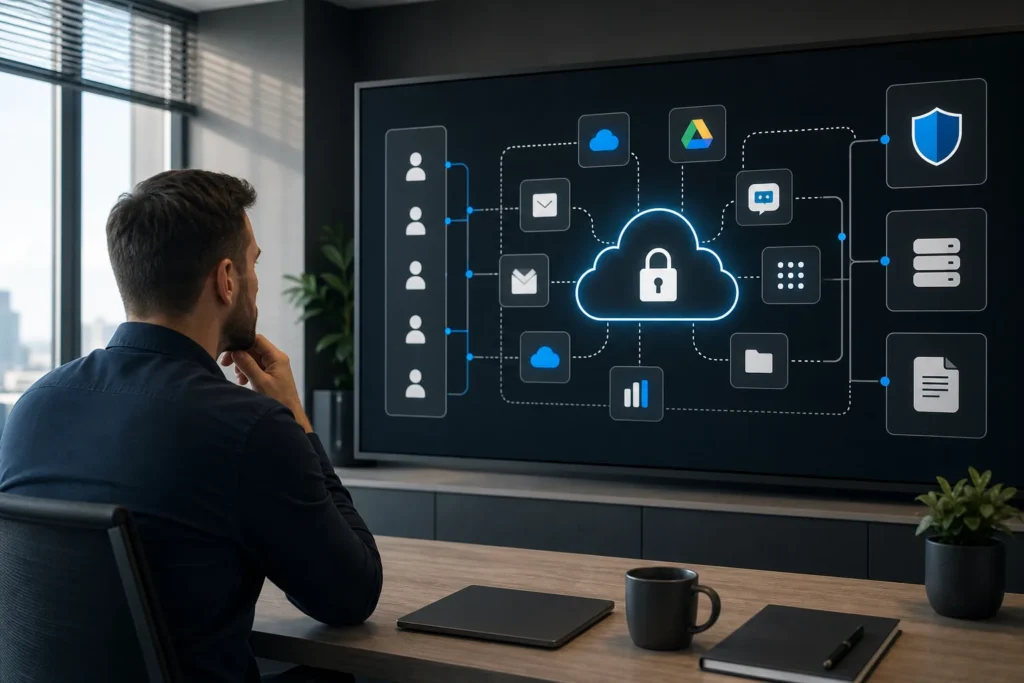
SaaS management often starts as a cost project. In regulated firms, that is too narrow. We need a plan that covers the gaps. These five steps give your team a working process for safer access, clearer costs, and stronger audit records. Table of Contents Step 1: Create a Complete SaaS Inventory Step 2: Classify SaaS […]
Managed IT Services Pricing: A How-To Guide
The biggest surprise in managed IT services pricing is often hidden in the quote. A low monthly fee may leave out security work your auditor expects. We’ll show you how to define your needs, compare pricing models, check compliance coverage, and review the contract before you choose. Table of Contents Step 1: Define Your IT, […]
Backup and Disaster Recovery: A Practical Guide
A backup can save a file. A disaster recovery plan must bring a business back to work. For regulated firms, the biggest warning sign isn’t a high-cost service agreement. It’s silence about the basics, such as backup method, RPO, and RTO. We use the steps below to build a plan that fits the risk, the […]
HIPAA Compliant Cloud Storage: How to Set It Up
Cloud storage can protect patient data, but a storage account alone doesn’t make a practice HIPAA compliant. You still need the right contract, settings, staff rules, and proof that controls work. We’ll show you how to set up HIPAA compliant cloud storage and keep it audit-ready. The process works for medical practices, home health teams, […]
How to Report a HIPAA Violation: 5 Steps
Finding out that your medical information was shared without permission can feel personal and frightening. We’ll show you how to report a HIPAA violation, preserve proof, notify the right person, and file with federal regulators when needed. Table of Contents Step 1: Confirm the Suspected HIPAA Violation and Preserve Evidence Step 2: Report Internally to […]
Business Process Automation: A How-To Guide
Automation can cut repeated work, but a faster process can still create a compliance problem. That risk is easy to miss in regulated work, where healthcare, finance, and law firms handle sensitive records every day. We use the five steps below to make business process automation safer, easier to test, and easier to explain during […]